The Digital Operational Resilience Act (DORA) marks a fundamental shift in how financial institutions define
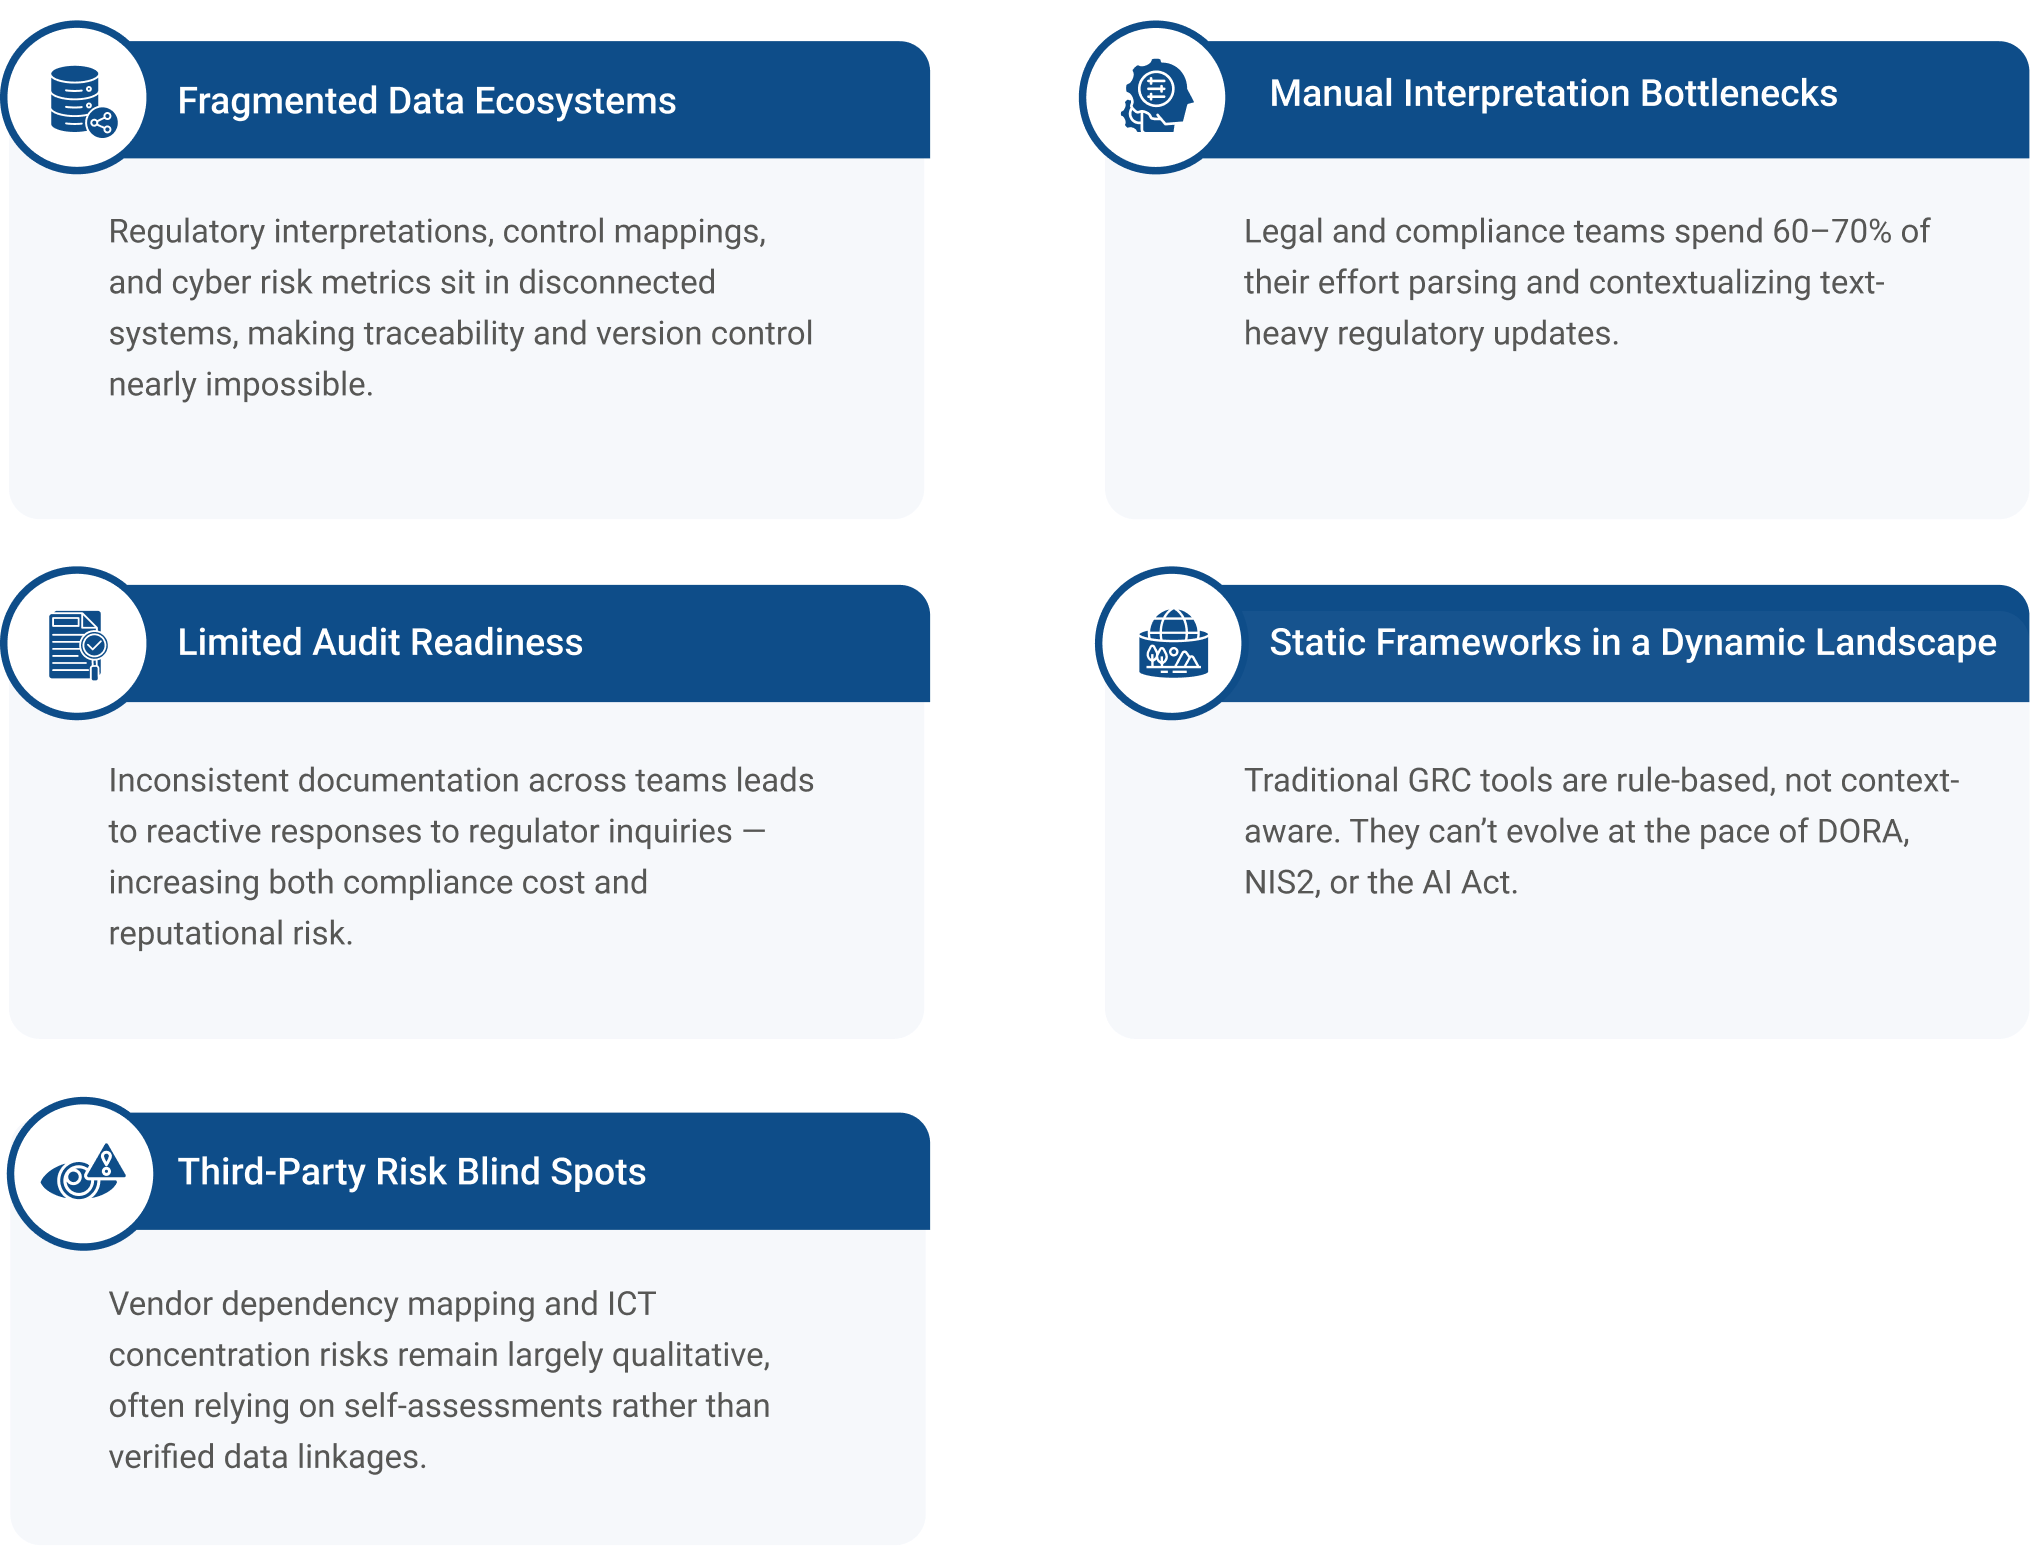
and maintain cyber resilience. No longer confined to IT or compliance, DORA demands a holistic, data-driven approach to managing operational risk — spanning governance, incident reporting, third-party oversight, and ICT continuity. Yet most banks are still navigating this change through fragmented tools, static spreadsheets, and manual processes.
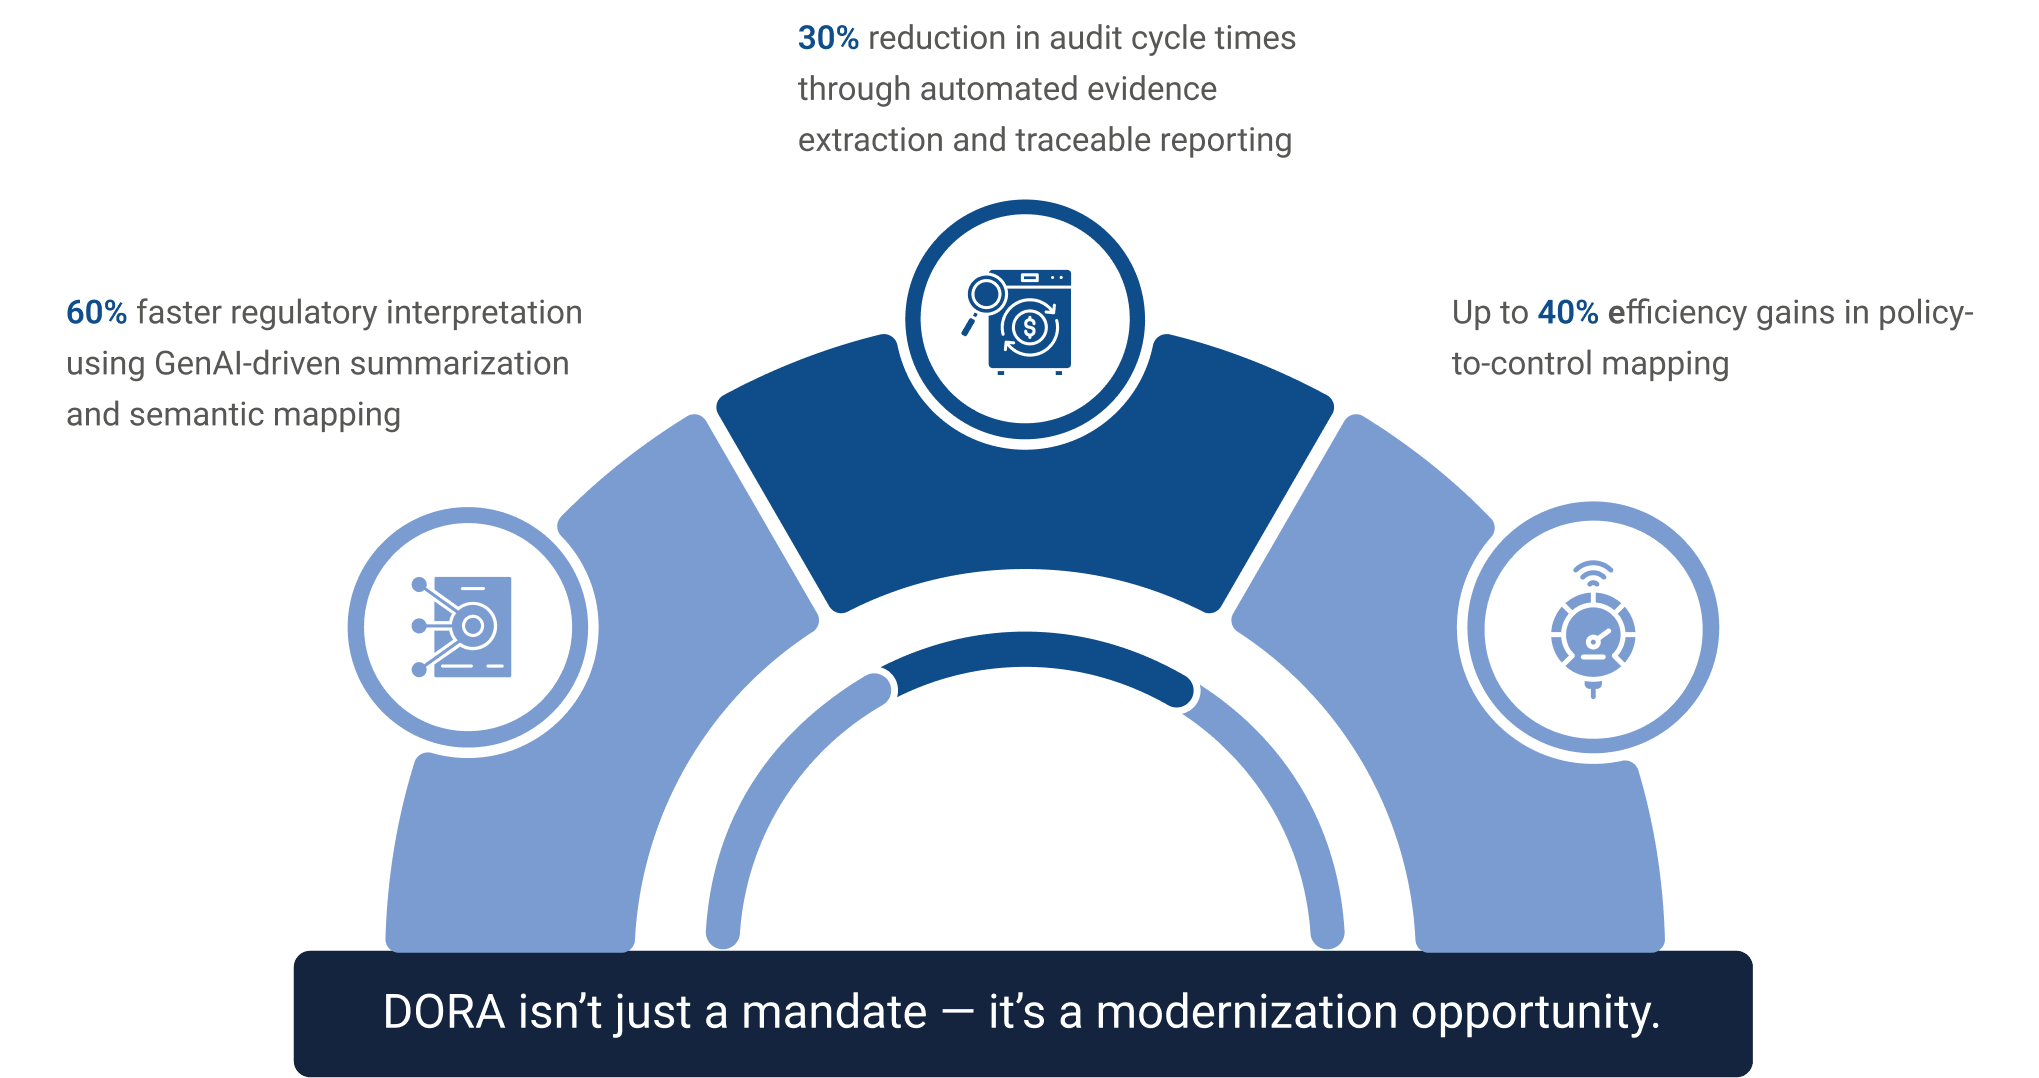
Apexon’s approach to regulatory change management transforms this paradigm by embedding Generative AI (GenAI) directly into the regulatory lifecycle. Our solution enables institutions to move from reactive compliance to predictive, continuous assurance — identifying control gaps before they surface, automating interpretation of new mandates, and creating real-time visibility across cyber, risk, and compliance functions.
This paper outlines the emerging industry challenges surrounding DORA implementation and explores how Apexon’s GenAI-enabled regulatory intelligence framework empowers financial institutions to build resilient, scalable, and audit-ready compliance ecosystems – safely and efficiently.